Automated HTTPS SSL Certificate Deployment & TLS Hardening
Zero-touch certificate lifecycle management with automated issuance, renewal, and TLS 1.3 enforcement across multi-cloud environments.
The Challenge
A global SaaS platform operated 500+ custom domains across 12 Kubernetes clusters on three cloud providers. Certificate renewals were manual, tracked in spreadsheets, and caused monthly outages when wildcard certs expired on edge nodes. TLS configuration drifted: some endpoints negotiated TLS 1.1, HSTS headers were inconsistent, and OCSP stapling was disabled. The security team spent 40+ hours per quarter on certificate fire-drills instead of hardening posture.
The Engineered Solution
Jampuk Intelligence deployed a GitOps-Native Certificate Automation Platform built on cert-manager, external-dns, and custom TLS policy controllers.
- → Unified Domain Inventory: External-dns syncs all ingress hostnames to a central CertificateRequest CRD, eliminating spreadsheet drift.
- → ACME DNS-01 Automation: Cert-manager solves challenges via cloud provider DNS APIs (Route53, Cloud DNS, Azure DNS), issuing ECDSA P-256/P-384 certs in parallel.
- → Policy-Driven TLS Hardening: Cluster-scoped TLSProfile CRDs enforce TLS 1.3-only, HSTS preload, OCSP stapling, and cipher allow-lists. Drift triggers GitOps alerts.
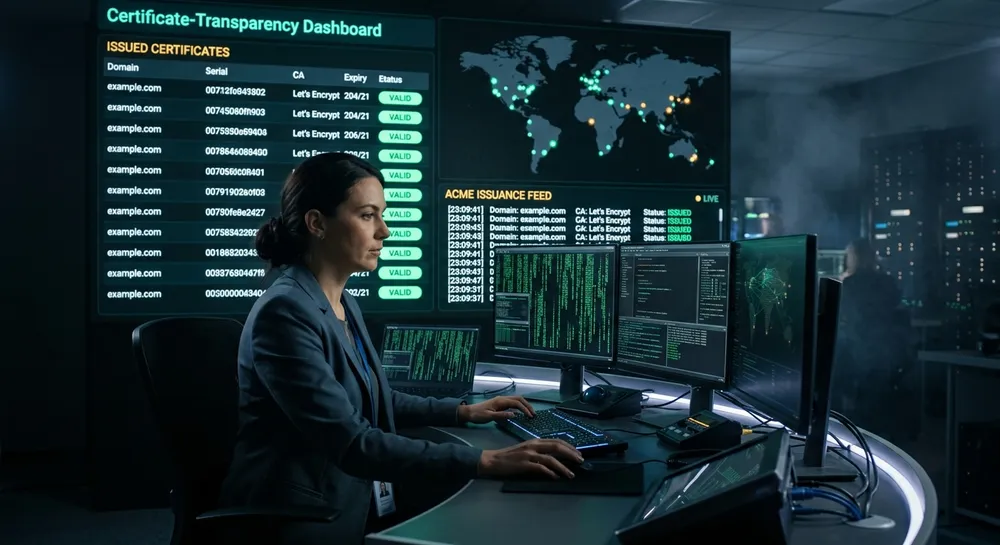
- → Certificate Transparency Monitoring: Custom controller watches public CT logs for mis-issuance, alerting on unauthorized certificates for owned domains within minutes.
- → Zero-Downtime Rotation: Pre-renewal 30 days before expiry, new certs stage in secret stores, ingress controllers reload via kubectl rollout without connection drops.
Certificate Lifecycle Automation Pipeline
From domain discovery to TLS 1.3 enforcement across multi-cloud edges
Domain Inventory & Validation
Discovers all apex and subdomains, validates DNS control via ACME challenges
Automated Issuance
Requests certificates from Let's Encrypt / ZeroSSL via cert-manager with DNS-01 challenge
Deployment & Binding
Injects certs into ingress controllers, load balancers, and edge caches with zero-downtime reload
Renewal & Rotation Loop
Monitors expiry, auto-renews 30 days prior, rotates keys, and validates OCSP stapling
Core Benefits & System Outcomes
Measured TLS automation outcomes with full cryptographic ownership
Zero-Touch Certificate Lifecycle
Eliminates manual CSR generation, validation emails, and paste-deploy cycles. Certificates issue, renew, and bind automatically across Kubernetes ingress, Cloudflare, AWS ALB, and Azure Front Door.
TLS 1.3 Only, HSTS Preload Ready
Enforces TLS 1.3 with modern cipher suites (TLS_AES_256_GCM_SHA384, TLS_CHACHA20_POLY1305_SHA256). HSTS with preload, OCSP stapling, and Certificate Transparency monitoring baked in by default.
Multi-Cloud, Multi-Domain at Scale
Manages 500+ domains across GKE, EKS, AKS, and bare-metal edges from a single GitOps repo. Wildcard and SAN certificates provisioned in parallel with per-environment policies.
TLS Certificate Issuance & Handshake Simulator
Replay automated certificate provisioning and observe the TLS 1.3 handshake
1. Select Target Environment
> Standing by. Initiate certificate issuance to observe ACME flow and TLS handshake...
Automate Your Certificate Lifecycle Before the Next Expiry
Speak directly with AI steward & systems architect Hafiz Zainudin to scope a fixed-price TLS automation delivery and eliminate certificate-related outages permanently.